Security Insights & Technical Guidance
How to Prepare Effective Security System Tender Specifications
Security procurement is vulnerable to ambiguity. If a tender says only “provide a suitable CCTV system,” bidders may propose fundamentally different solutions while all claiming compliance. The result can be difficult evaluation, expensive variations and disputes about what the contractor was required to deliver. A well-structured security tender makes the purpose, boundaries and performance expectations clear before prices are compared.
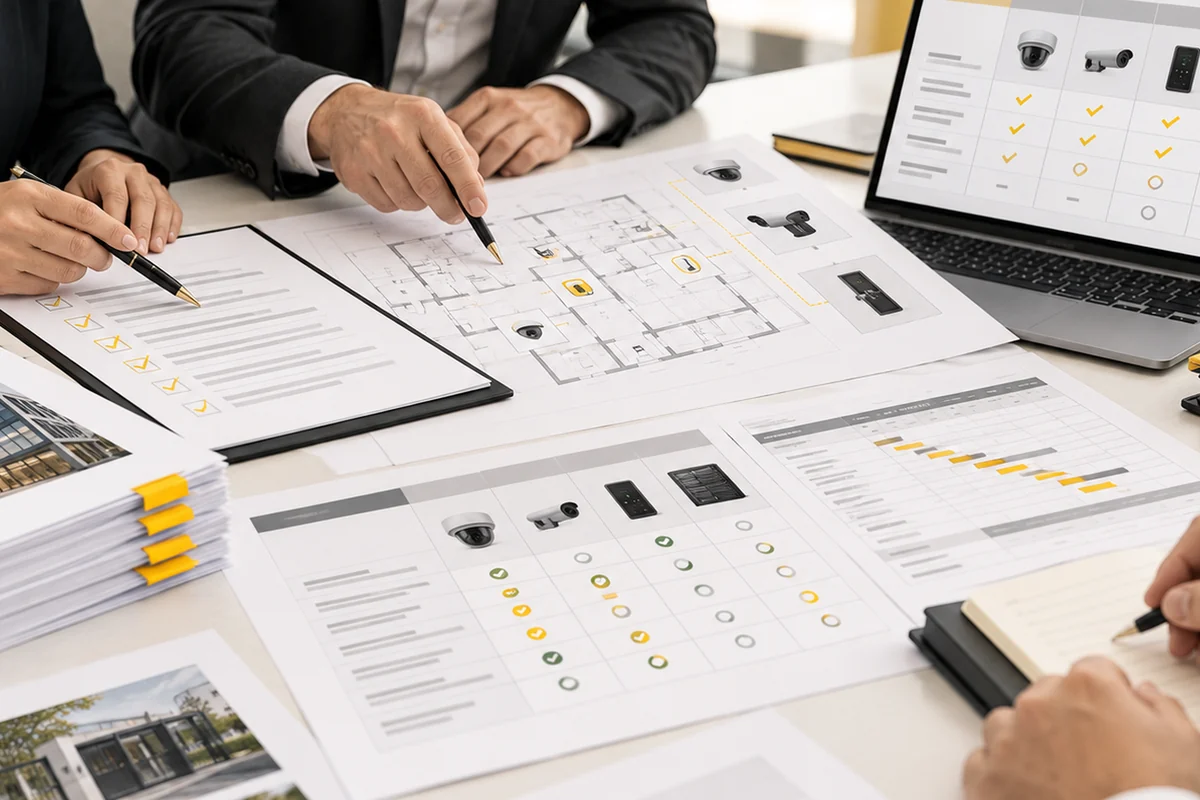
Security procurement is vulnerable to ambiguity. If a tender says only “provide a suitable CCTV system,” bidders may propose fundamentally different solutions while all claiming compliance. The result can be difficult evaluation, expensive variations and disputes about what the contractor was required to deliver. A well-structured security tender makes the purpose, boundaries and performance expectations clear before prices are compared.
The documents should link the client’s assessed risks and operating requirements to measurable outputs. An excellent tender is not necessarily the longest document or the most prescriptive catalogue of equipment; it is the one that gives suitable bidders enough information to propose a comparable solution and gives the client objective criteria for evaluation and acceptance.
1. Define the procurement basis
Before drafting a request for proposal, the project team should establish site scope, approved design stage, assets to be protected, operating model, interfaces with other contracts and financial or programme constraints. A TVRA or security master plan may identify the required protective objectives, while approved drawings and user requirements translate them into project scope.
Identify whether the tender is for design consultancy, product supply, installation, integration, maintenance, guarding-related technology or a combined design-and-build engagement. Each creates different responsibilities. The procurement documents should state what the owner supplies, what the contractor designs and which approvals are required before installation.
2. Write performance requirements that can be tested
Use objective functional language where possible: what an authorized user must be able to do, what information the operator must receive, what event must be recorded and which system interface must work. Avoid claiming a particular commercial product automatically delivers a protective outcome. Specified products or equivalents, where permitted, should be evaluated against defined functional and technical criteria.
For surveillance, for example, differentiate the viewing task, image usability, recording retention, synchronization and export requirements. For access control, clarify controlled zones, permission administration, monitoring, interfaces and abnormal operating modes. Define assumptions about networks, cybersecurity responsibilities and access to existing systems.
3. Develop coordinated technical documents
The tender package may include the following, with exact requirements determined by contract and design maturity:
| Document | Primary purpose | Common omission |
|---|---|---|
| Scope of work | Establish inclusions, exclusions and boundaries | Ambiguous contractor responsibilities |
| Operational requirements | Explain security tasks and user workflows | Product list without operating outcomes |
| Technical specifications | Set functional, performance and installation standards | Requirements impossible to test |
| Design drawings | Locate equipment and define relevant interfaces | Drawings inconsistent with schedule |
| BOQ / pricing schedule | Enable comparable commercial responses | Unclear allowances and exclusions |
| Interface matrix | Identify system-to-system responsibilities | No owner for cross-system integration |
| Compliance schedule | Require evidence-based bidder response | “Comply” without supporting explanation |
| Test and handover schedule | Define how completion will be verified | Testing deferred until after installation |
The Bill of Quantities (BOQ) needs a defined relationship with drawings and technical schedules. Quantities may be fixed, provisional or subject to site verification; their contractual status must be explicit.
4. Require a meaningful bidder response
Tender instructions should describe how bidders must submit their technical proposals, staff and subcontractor information, programme, product schedules, warranties, deviations and clarifications. Require bidders to identify exceptions to each material specification rather than hiding them in marketing brochures.
A structured compliance matrix can distinguish compliance, partial compliance and non-compliance, supported by document references. Avoid implying that a self-declaration is proof of installed performance.
Illustrative compliance matrix
| Requirement ID | Requirement | Bidder response | Evidence requested |
|---|---|---|---|
| VMS-01 | Authorized operator can retrieve event-related recorded video | Comply / Partial / Exception | Functional demonstration or product documentation |
| ACS-02 | Administrative changes are logged and attributable | Comply / Partial / Exception | System capability and configuration approach |
| INT-03 | Agreed alarm triggers associated operator view | Comply / Partial / Exception | Interface method and test case |
| DOC-04 | Submit as-built documents and operating manuals | Comply / Partial / Exception | Handover deliverable schedule |
A real project should replace these examples with precise, approved and testable requirements.
5. Build transparent evaluation criteria
Evaluation criteria may cover technical compliance, functional quality, integration, maintainability, implementation approach, team competence, delivery risk, commercial terms and total lifecycle cost. Relative weights and mandatory conditions should be set before reviewing proposals, consistent with the procurement regime that applies to the purchaser.
Do not compare headline prices without reconciling omissions, maintenance costs, licensing, software subscriptions, spare parts and assumptions about existing infrastructure. A low bid that excludes critical interfaces or testing can be a poor commercial outcome.
6. Manage clarification and deviations
During tender evaluation, questions should be logged and responses communicated appropriately to preserve fairness under the applicable procurement process. Material ambiguities may need written clarification or revised documents rather than informal assumptions. Record accepted deviations and their implications for risk, functionality, cost and future maintenance.
Tender recommendations should explain why a proposal meets or does not meet requirements and identify unresolved technical risks. The consultant supports the owner’s evaluation; award authority remains with the appropriate client decision-maker.
7. Specify testing before construction begins
Acceptance requirements should be included in the tender, not invented at the end of the project. Define planned FAT, SAT, integrated tests, defect classification, retesting, documentation and training. A camera powering on is not sufficient evidence that a security monitoring use case functions correctly; system-level verification may be needed.
An Acceptance Test Procedure (ATP) should document prerequisites, test description, expected result, observed evidence and sign-off responsibilities. For interfaces, test both normal event handling and agreed failure conditions.
8. Make handover and support part of the contractual deliverable
A security system remains operational long after installation. Define operator training, maintenance schedules, spare parts, configuration backups, administrator privileges, cybersecurity responsibilities, warranty terms and O&M manuals. Clarify software updates, licensing renewal and support response obligations where applicable. Ownership of recordings, data and configurations should be addressed explicitly.
9. Common tender mistakes
Using manufacturer brochures as specifications; issuing inconsistent drawings and BOQ; omitting cybersecurity or networking boundaries; ignoring integration requirements; accepting non-evidenced “full compliance”; comparing non-equivalent scopes; failing to specify testing; and leaving operator training or maintenance undefined. Each of these creates a mismatch between the buyer’s expectation and the contractor’s deliverable.
Frequently asked questions
Should a tender name a preferred manufacturer?
This depends on applicable procurement rules and justified technical requirements. Performance-based alternatives can improve comparability and competition when appropriate; existing system compatibility may also be a legitimate constraint that needs documentation.
Is the lowest price the best value?
Not necessarily. A meaningful comparison should account for scope, compliance, implementation risk, integration and lifecycle costs under the buyer’s approved evaluation method.
What is the consultant’s role after award?
Depending on appointment, it may include submittal review, construction-stage oversight, testing, defect management and handover verification. These should be stated in the consultancy scope.
Singapore procurement context
Private owners, public agencies and designated developments may face different contractual and regulatory obligations. Do not copy procurement requirements from another jurisdiction into a Singapore tender without checking applicability. The statutory Security-by-Design process applies to developments or infrastructures designated by the Minister for Home Affairs as Special Developments or Special Infrastructures. For a designated project, coordinate security documentation with the Infrastructure Protection Act process and the approved Security Plan: https://www.police.gov.sg/Knowledge-Hub/Infrastructure-Protection/Special-Developments-Special-Infrastructures. This reference is not a substitute for legal or procurement advice.
The UK NPSA operational-requirements guidance illustrates how end-user needs can be converted to performance specifications: https://www.npsa.gov.uk/security-best-practices/protective-security-risk-management-psrm/operational-requirements. It is non-statutory UK technical guidance, not Singapore legal or procurement requirements.
Next step: Explore Security Tender Consultancy, Security Design and Project Management.
Speak with LORIN
Discuss a Security Requirement
Discuss how this guidance applies to a defined facility, development or security decision.