LORIN service
Threat, Vulnerability & Risk Assessment
A useful TVRA gives management a defensible basis for deciding which risks matter, how effective existing controls are and which mitigation measures should be prioritised. It is more than a checklist or a list of security equipment.
Why this matters
Risk Assessment That Prioritises Credible Exposure
Establish a defensible basis for deciding which risks matter and what to address first.
Clients may need to understand where physical-security exposure exists before changing controls, investing in technology, planning a development or reviewing an existing programme.
A TVRA is a focused risk-assessment activity. It is distinct from the broader security master-planning process, although its findings can inform one.
Method
Assessment methodology
Agree scope, risk criteria and critical assets; develop credible scenarios; review site layout, boundaries, personnel movements, guarding, CCTV, access control, emergency procedures and relevant operational practices; evaluate consequence and likelihood under the agreed methodology; then identify treatment options, risk owners and residual exposure.
- 01
Establish site, asset and operating context
- 02
Identify credible threat scenarios
- 03
Review vulnerabilities and existing controls
- 04
Consider consequences and risk
- 05
Recommend proportionate improvements
- 06
Reassess risk when changes are made
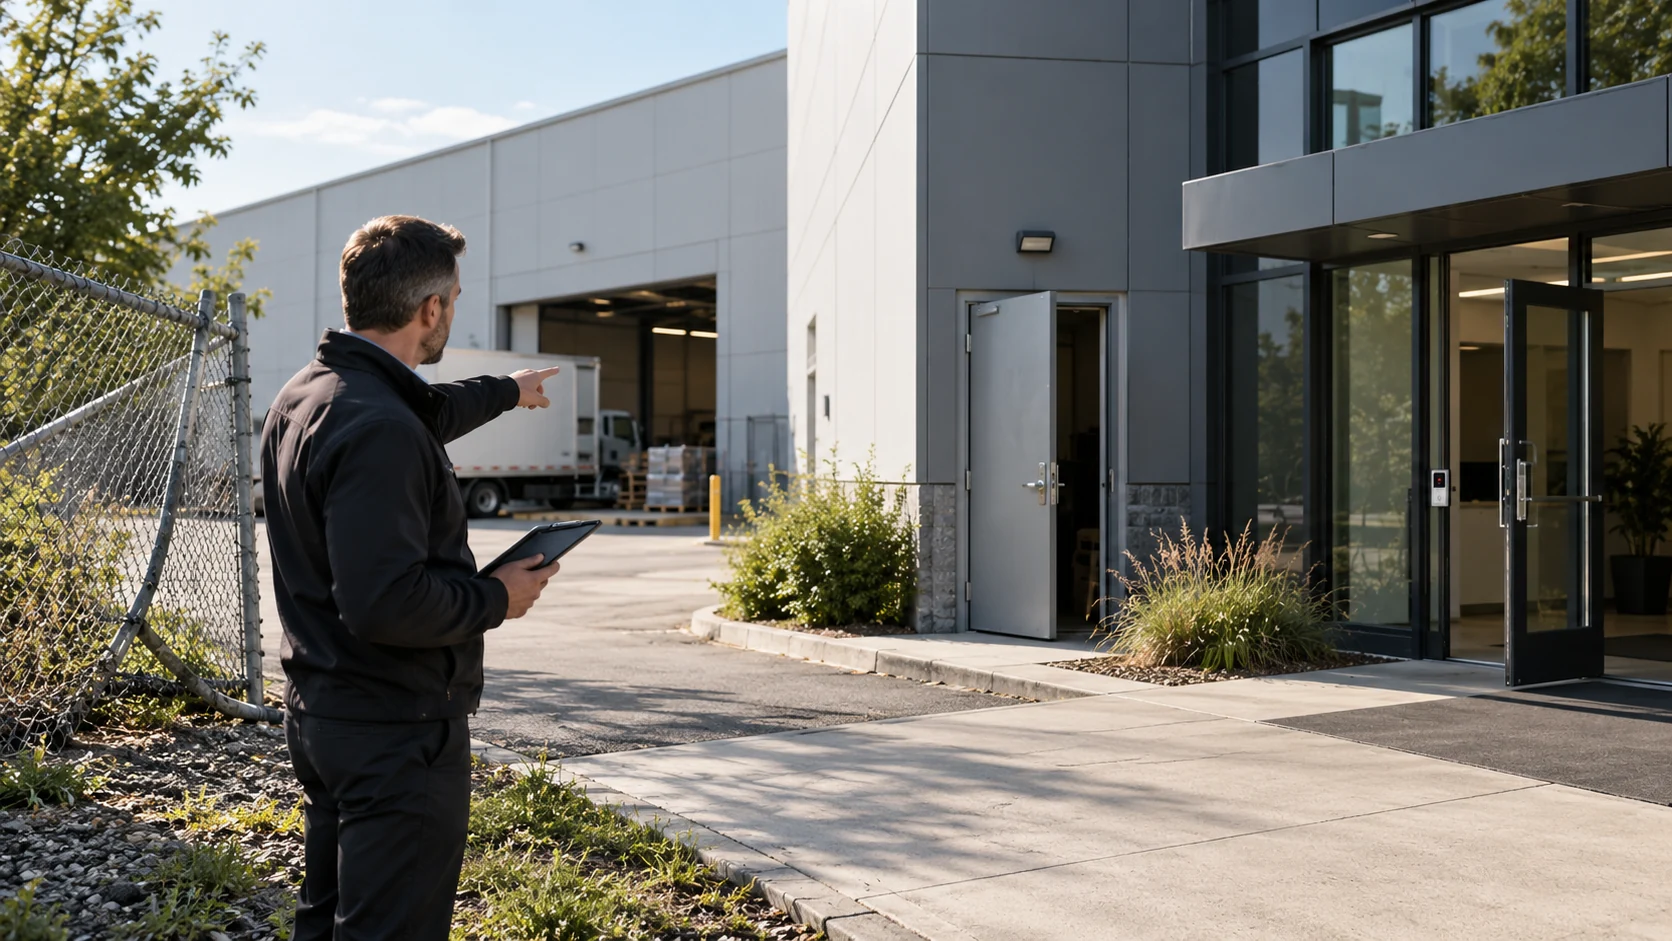
Consulting in practice
Specific consulting scope
A useful TVRA gives management a defensible basis for deciding which risks matter, how effective existing controls are and which mitigation measures should be prioritised. It is more than a checklist or a list of security equipment.
- Facility or operational security review
- Threat and vulnerability analysis
- Existing-control assessment
- Risk and consequence considerations
- Improvement recommendations
- Reassessment following agreed improvements
Scope and deliverables
What LORIN Reviews and Designs.
The scope may include document review, stakeholder discussion, site inspection and analysis of how controls operate in practice. Outputs are calibrated to the client’s decision and the engagement brief.
Facility or operational security review
Threat and vulnerability analysis
Existing-control assessment
Risk and consequence considerations
Improvement recommendations
Reassessment following agreed improvements
Typical outputs
What You Receive.
Relevant experience
Recorded project material includes risk assessment and security-survey work for NETS Cards centres, KPLC, SGX planning and other complex facilities.
Frequently asked questions
Frequently Asked Questions.
What does a TVRA include?
A TVRA defines the assessment scope, critical assets, credible scenarios, vulnerabilities, existing controls, transparent risk ratings and prioritised treatment options.
How does a TVRA differ from detailed design?
A TVRA establishes the risk basis and required outcomes. Detailed design translates those outcomes into coordinated zoning, systems, procedures and acceptance requirements.
When should a facility be reassessed?
Reassessment is appropriate when there are material changes to the facility, assets, operating model, threat context, incidents or planned protective measures.
Speak with LORIN
Request a TVRA Proposal
Discuss the facility, decision and project stage with a LORIN consultant.